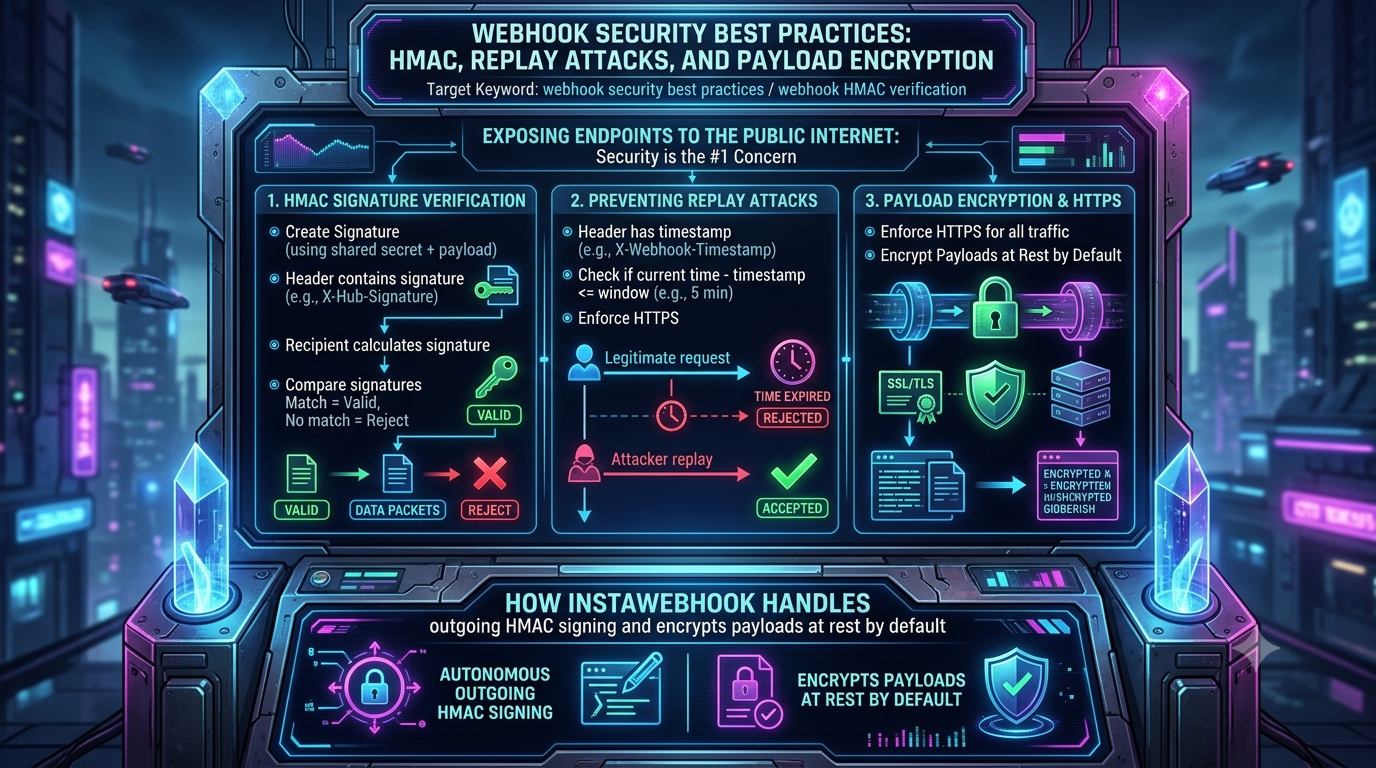
Ingress Security & Cryptographic Verification: Enterprise Webhook Hardening Guide

Learn how to secure webhook ingress with NIST post-quantum standards (ML-DSA) and protect outbound senders against BGP hijacking and DNS spoofing using DANE and TLSA.
Blog category
Articles grouped under Webhook Security.

Learn how to secure webhook ingress with NIST post-quantum standards (ML-DSA) and protect outbound senders against BGP hijacking and DNS spoofing using DANE and TLSA.

Master webhook ingress security, rate limiting, and traffic resiliency. Learn how to implement adaptive token bucket rate limiting, defend against DoS and Slowloris vectors, and solve dynamic origin

Learn how to build resilient callback receivers for LangChain and CrewAI webhooks. Master deterministic routing, handle non-deterministic LLM responses, and protect session states in async AI

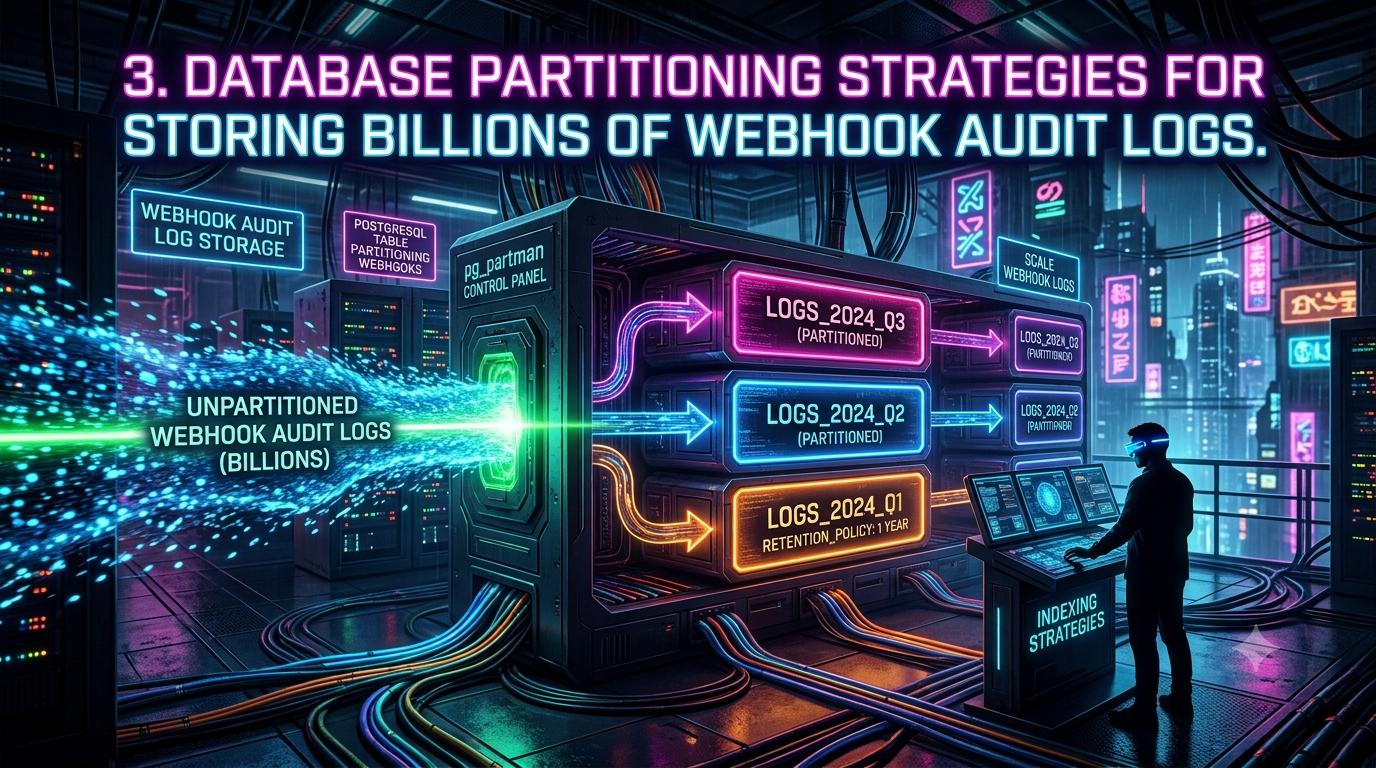
Storing Billions of Webhook Audit Logs in PostgreSQL: Partitioning, Indexing, Compression, and Retention Every SaaS platform that sends or receives webhooks eventually needs a...

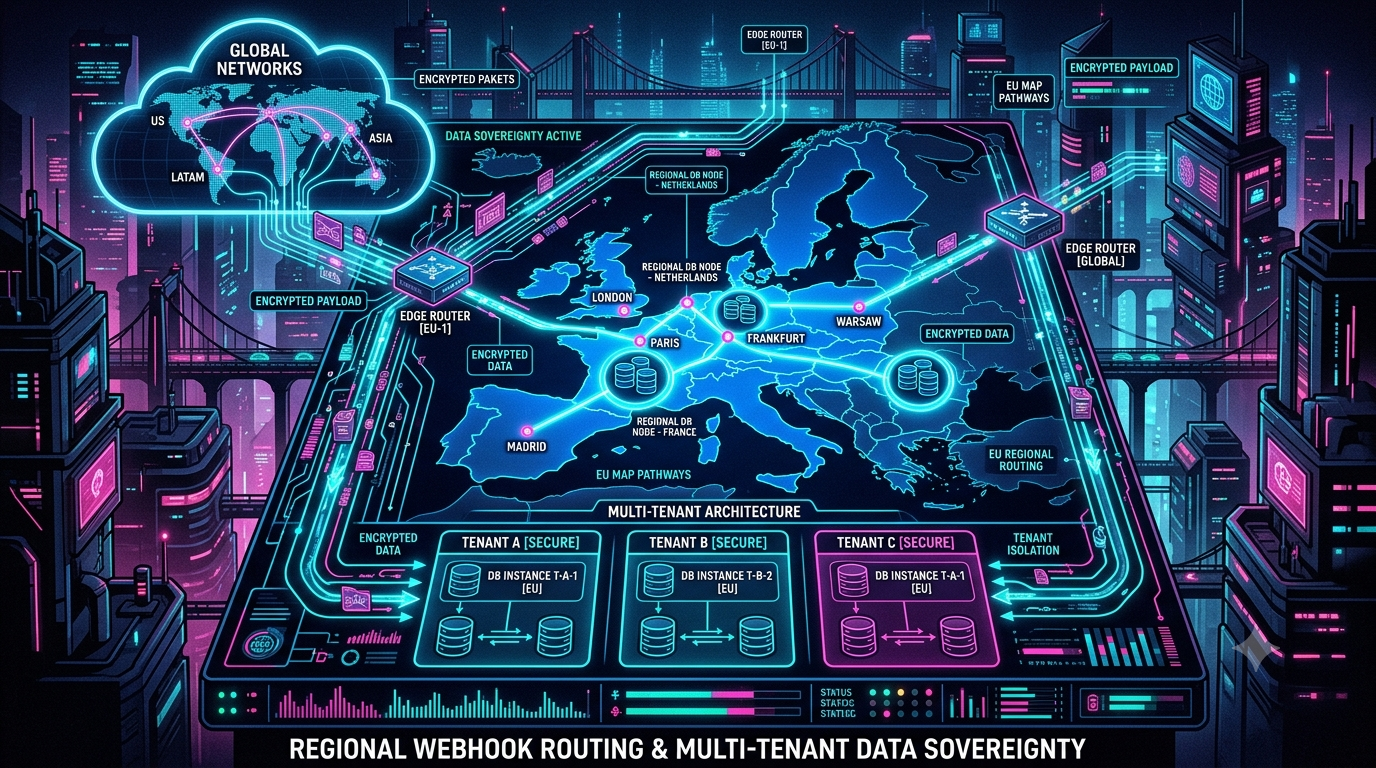
Multi-Tenant Data Sovereignty: Routing and Storing Regional Webhooks Securely Executive Summary Global SaaS platforms now operate under a growing patchwork of regional data rules...

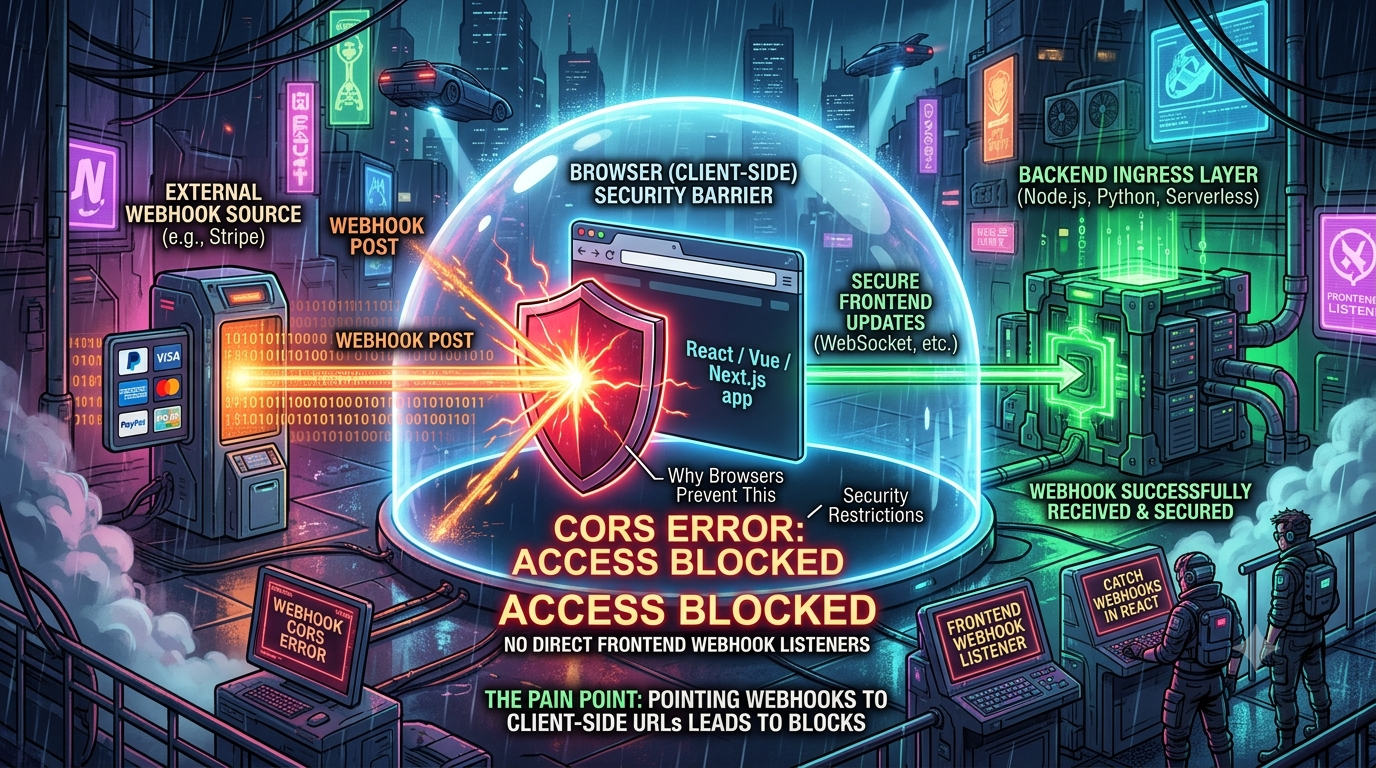
Why Your Browser Blocks Webhook Endpoints: CORS and Frontend Security It's a rite of passage for many junior and frontend developers: you're building an e-commerce store or a SaaS...

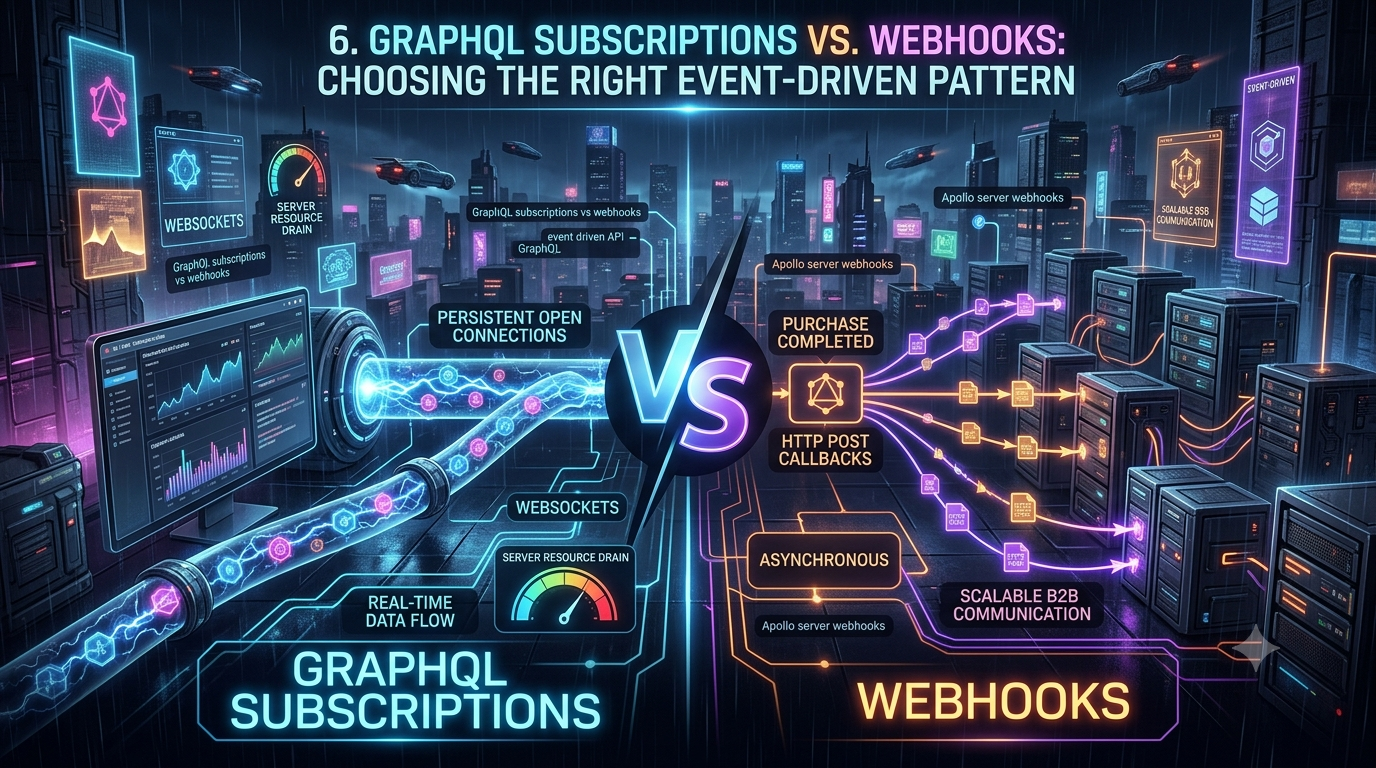
GraphQL Subscriptions vs. Webhooks: Choosing the Right Event-Driven Pattern When you're designing an event-driven API, one of the biggest architectural decisions is how you...

Protecting Webhook Endpoints from Replay Attacks (And Why Timestamps Aren't Enough) Last updated: September 21, 2026 Webhook signatures and timestamps stop forged and stale...

Taming "At-Least-Once" Delivery: Idempotent Webhook Ingestion in PostgreSQL Webhooks are how payment processors, commerce platforms and card issuers keep your system in sync with...

Building a Custom Webhook Provider: API Design Lessons from Stripe and GitHub Fact-checked against the official Stripe, GitHub and Standard Webhooks documentation in September...

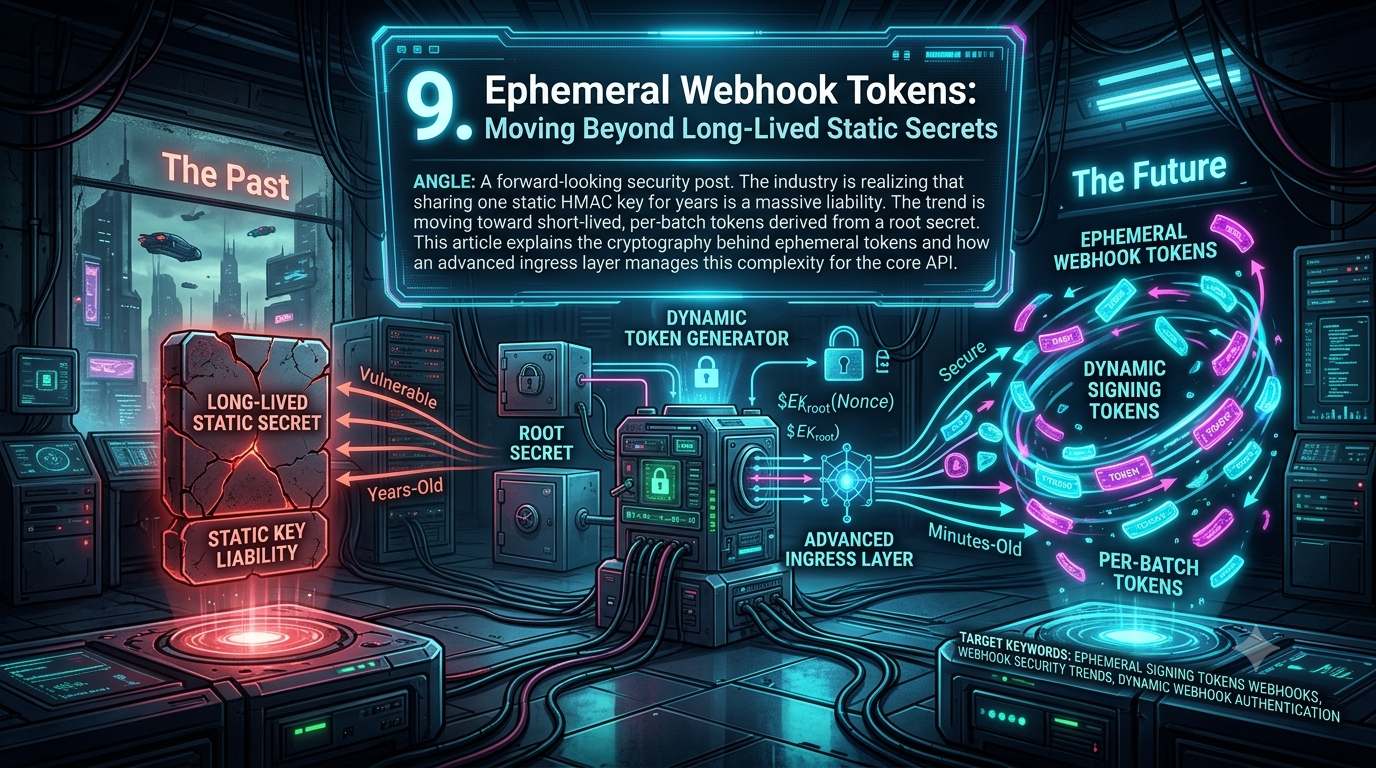
Ephemeral Webhook Tokens: Moving Beyond Long-Lived Static Secrets Introduction: The Fragile State of Webhook Security Webhooks are the connective tissue of modern event-driven...

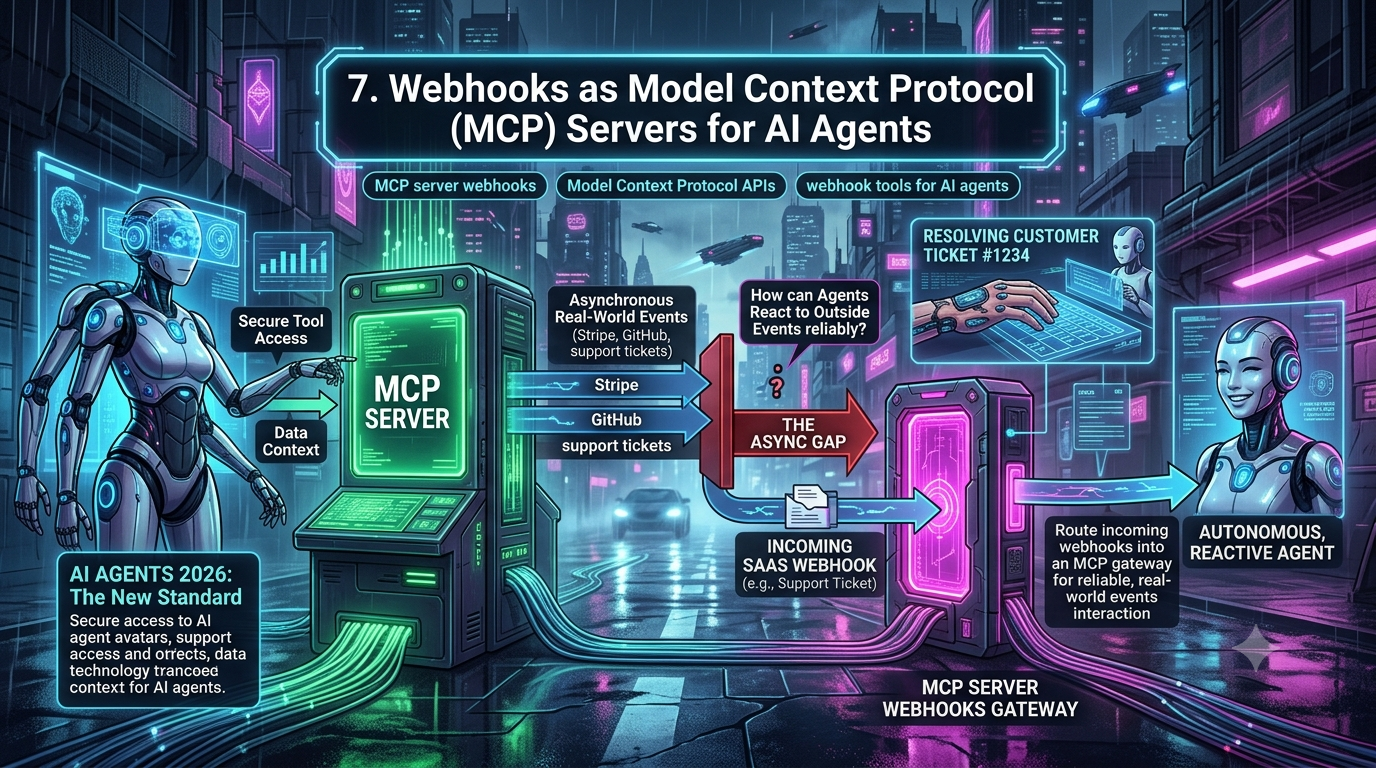
Webhooks and the Model Context Protocol: Building Event-Driven AI Agents The shift from chat-based LLMs to autonomous AI agents has exposed a structural bottleneck: most tool...

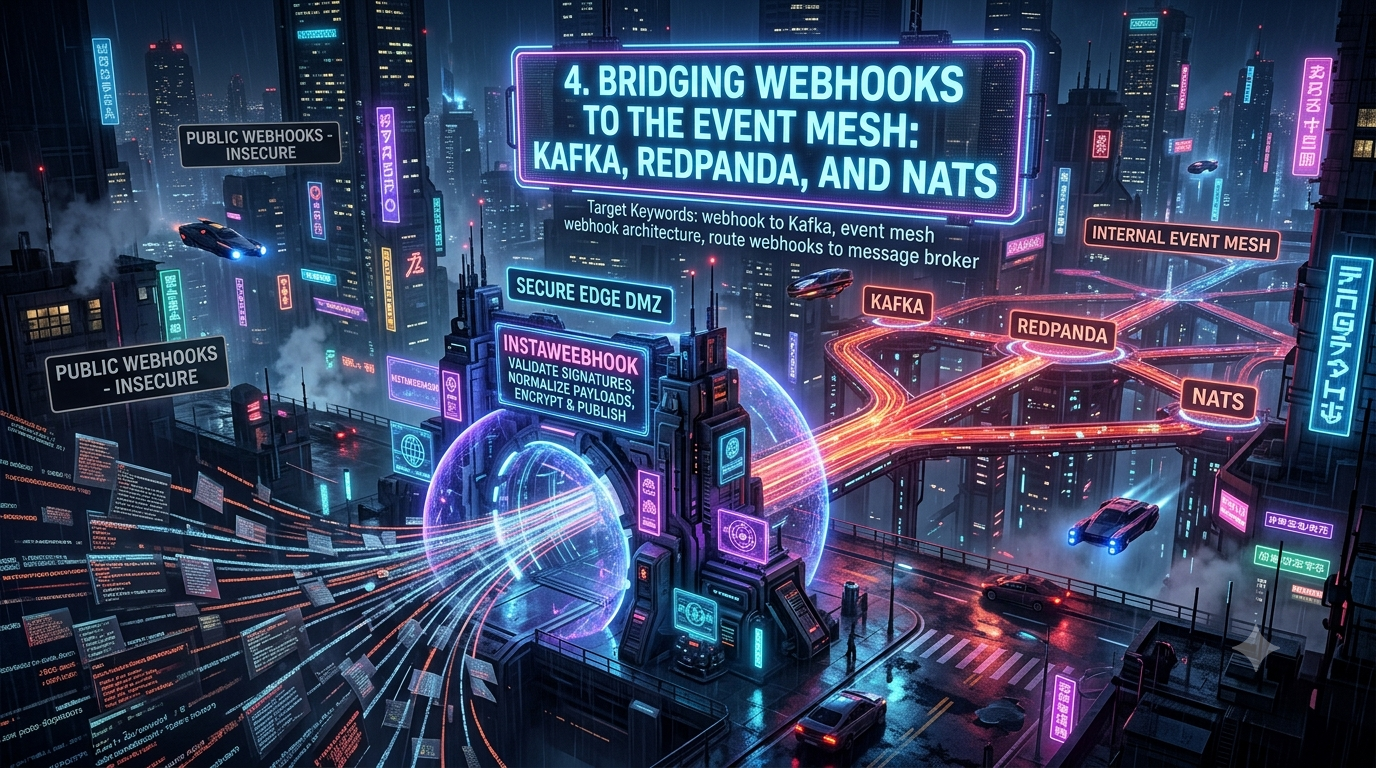
Bridging Webhooks to Your Event Mesh: A Secure Edge Pattern for Kafka, Redpanda, and NATS Every SaaS-heavy stack eventually hits the same wall: Stripe, GitHub, Shopify, and a dozen...

Bridging External Webhooks to Your Internal Event Mesh: A Secure Edge Gateway Pattern Every SaaS platform your company depends on — Stripe, GitHub, Shopify, Twilio — talks to you...

Building Async-First APIs: The 202 Accepted Pattern for the AI Era For a decade, most web APIs followed one rule: a client sends a request, the server does the work, and a status...

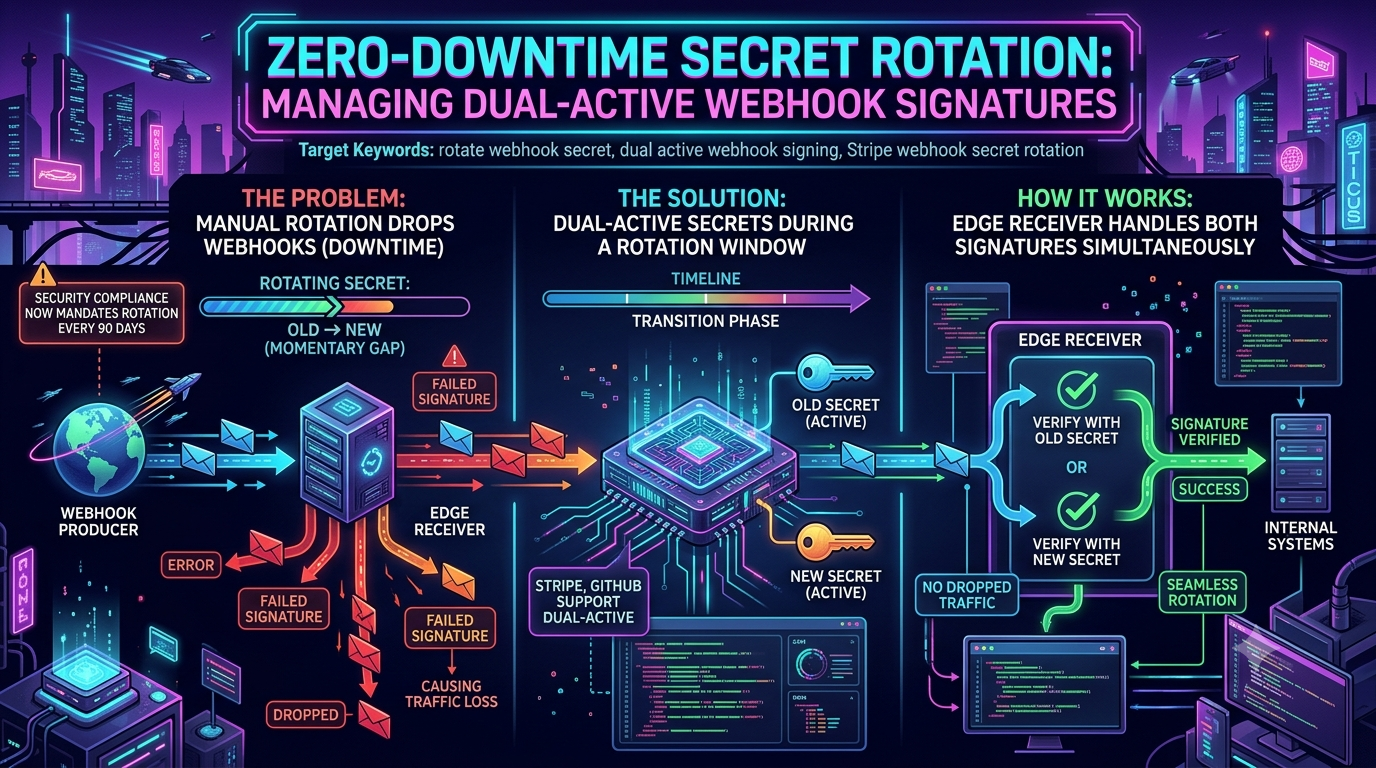
Zero-Downtime Secret Rotation: How to Manage Dual-Active Webhook Signatures In modern Cloud Native and DevOps environments, credential management is heavily regulated.

RFC 9421 and the Future of Webhook Signatures: What's Actually Changing For over a decade, event-driven web architecture has relied on an uncoordinated patchwork of proprietary...

Webhook Versioning: How to Stop Schema Changes From Breaking Your Integrations Webhooks look simple on the surface — a provider POSTs some JSON to your URL when something happens.

Catching Every Alert: Building a Zero-Loss Webhook Pipeline for Datadog, PagerDuty, and Grafana In modern Site Reliability Engineering (SRE), the line between observability and...

DORA and NIS2 Compliance: Auditing Webhook Delivery and Audit Logs The enforcement era for the European Union's two flagship cybersecurity and operational-resilience laws is no...

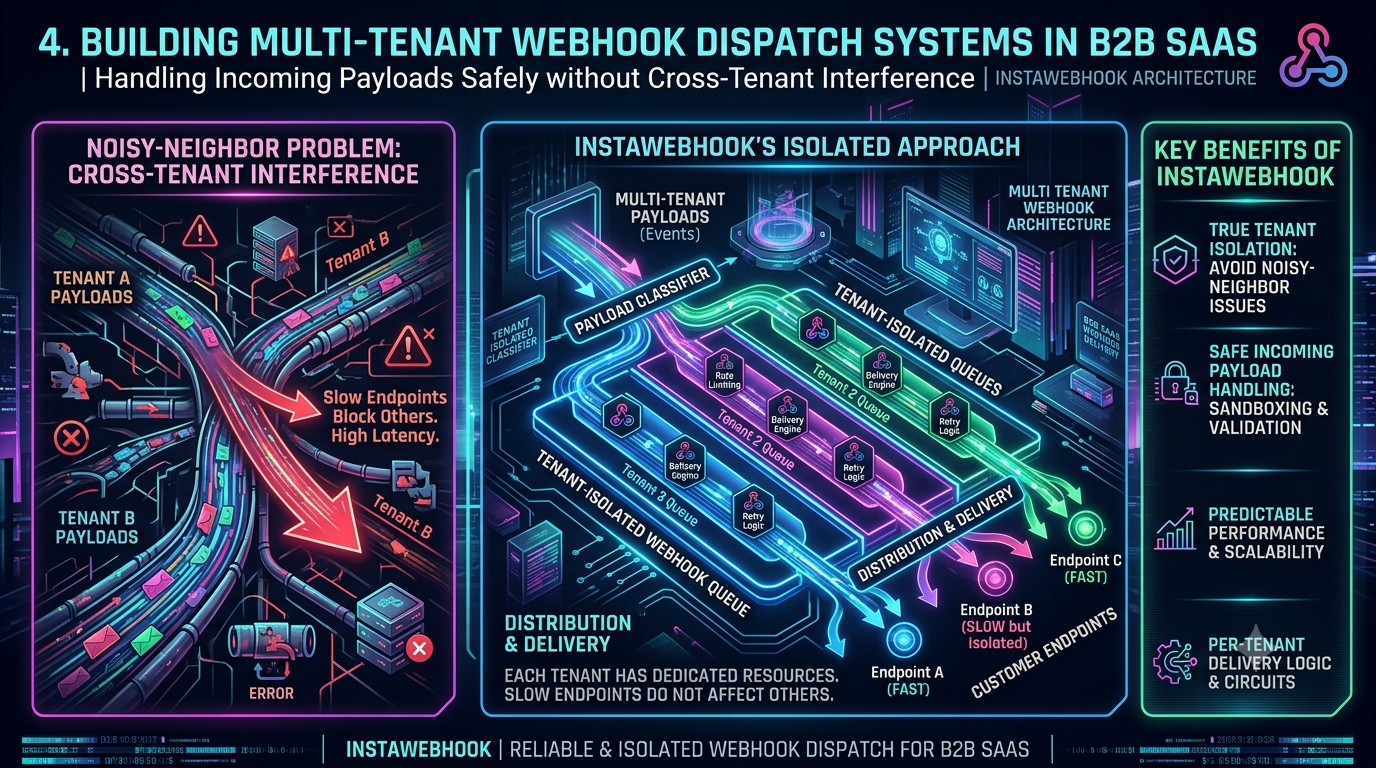
Building Multi-Tenant Webhook Dispatch Systems in B2B SaaS In modern B2B SaaS platforms, webhooks are the connective tissue between your core product and the rest of an enterprise...

Static IPs vs. Signatures: Meeting Enterprise Webhook Security Requirements Closing a B2B enterprise deal frequently stalls during the Information Security (InfoSec) review.

Automating Webhook Testing in Your CI/CD Pipeline (GitHub Actions & GitLab CI) Modern software delivery relies heavily on event-driven architecture.

Preventing Revenue Leakage: Securing Chargebee and Paddle Billing Webhooks Stripe dominates most developer conversations about online payments, but thousands of scaling SaaS...

Managing High-Volume Blockchain Webhooks: Architecture, Retries, and Event Queuing at Scale In Web2 architecture, webhooks arrive in a steady trickle.

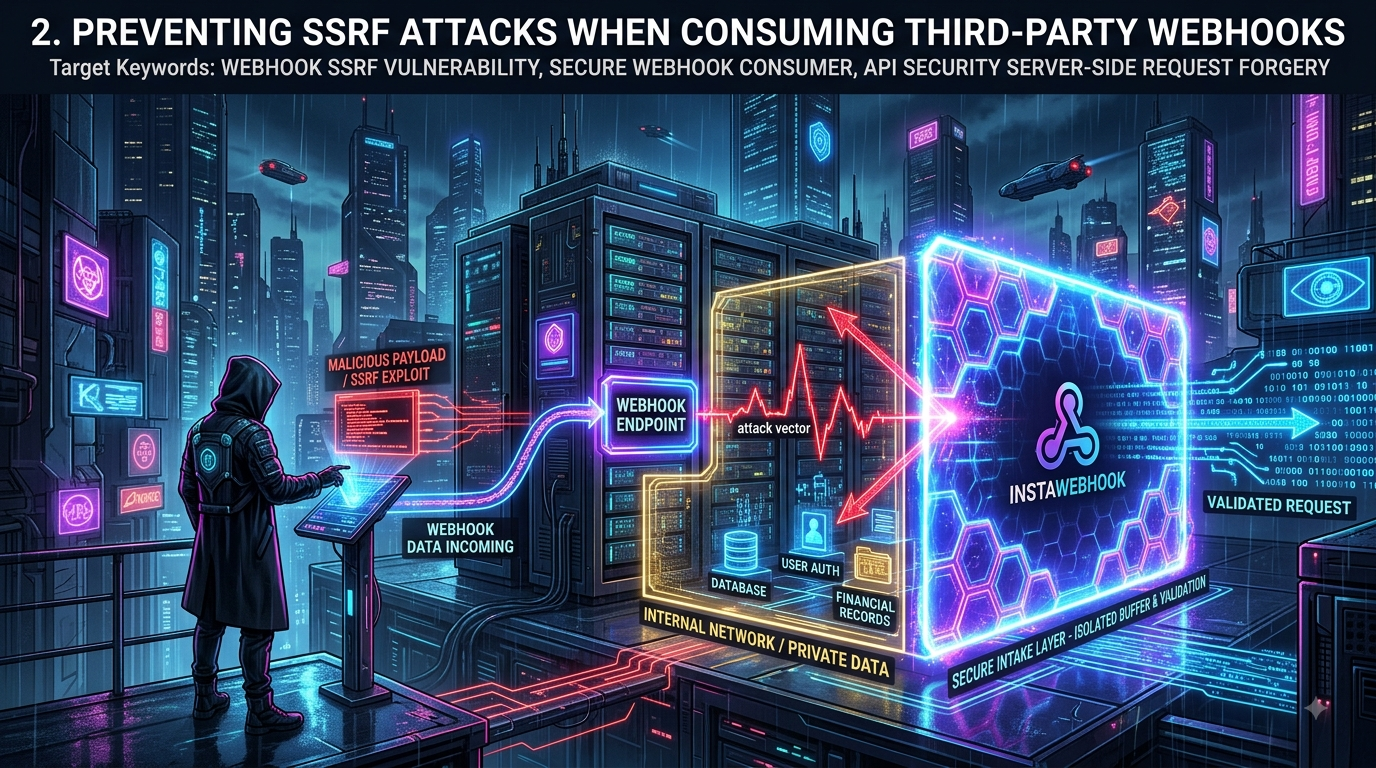
Preventing SSRF Attacks When Consuming Third-Party Webhooks: A Developer's Security Deep Dive In modern cloud architectures, webhooks are the connective tissue of asynchronous...

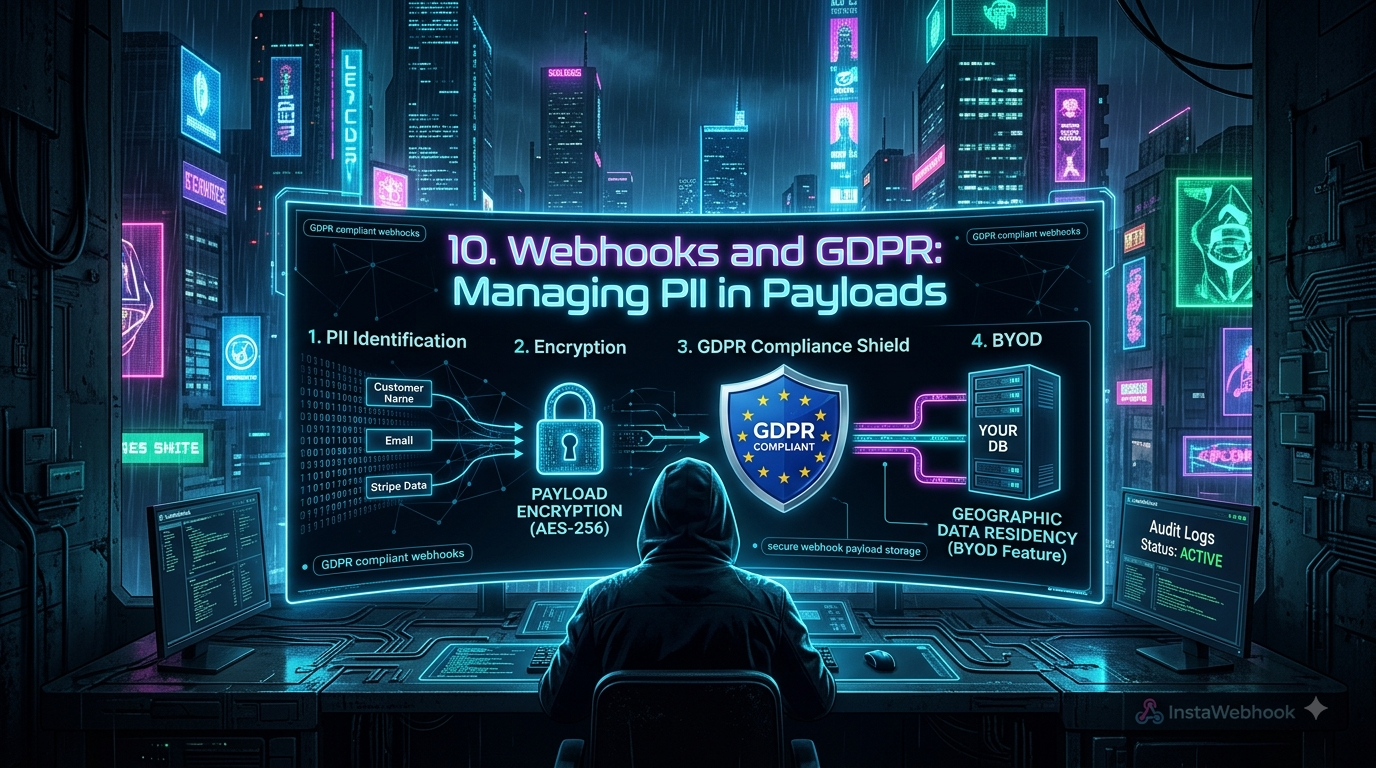
Webhooks and GDPR: Managing Personally Identifiable Information in Payloads Modern web development runs on event-driven architecture.

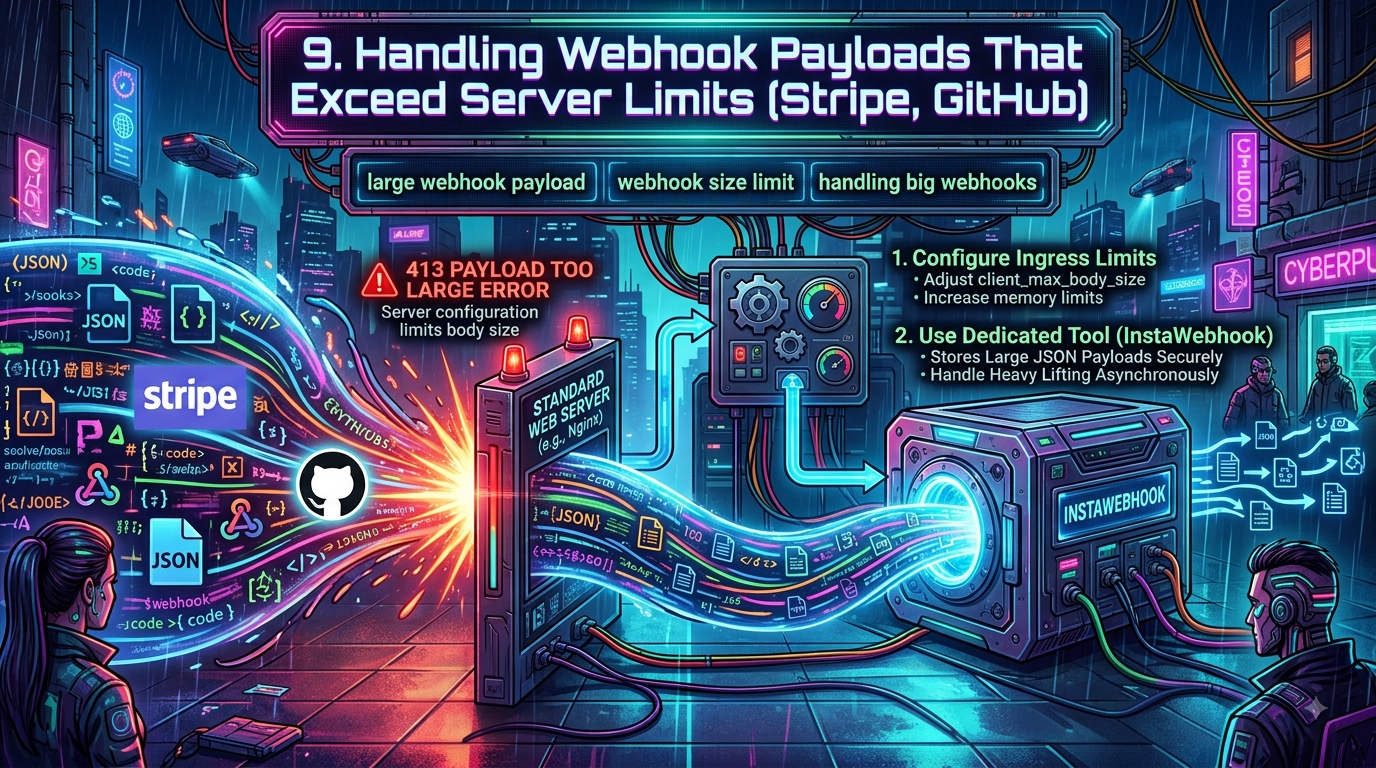
Handling Webhook Payloads That Exceed Server Limits (Stripe, GitHub & Beyond) Webhooks are the backbone of event-driven architecture.

The Danger of Exposing Your Main API to Third-Party Webhooks (And How to Fix It) As modern web applications become increasingly event-driven, third-party webhooks have become the...

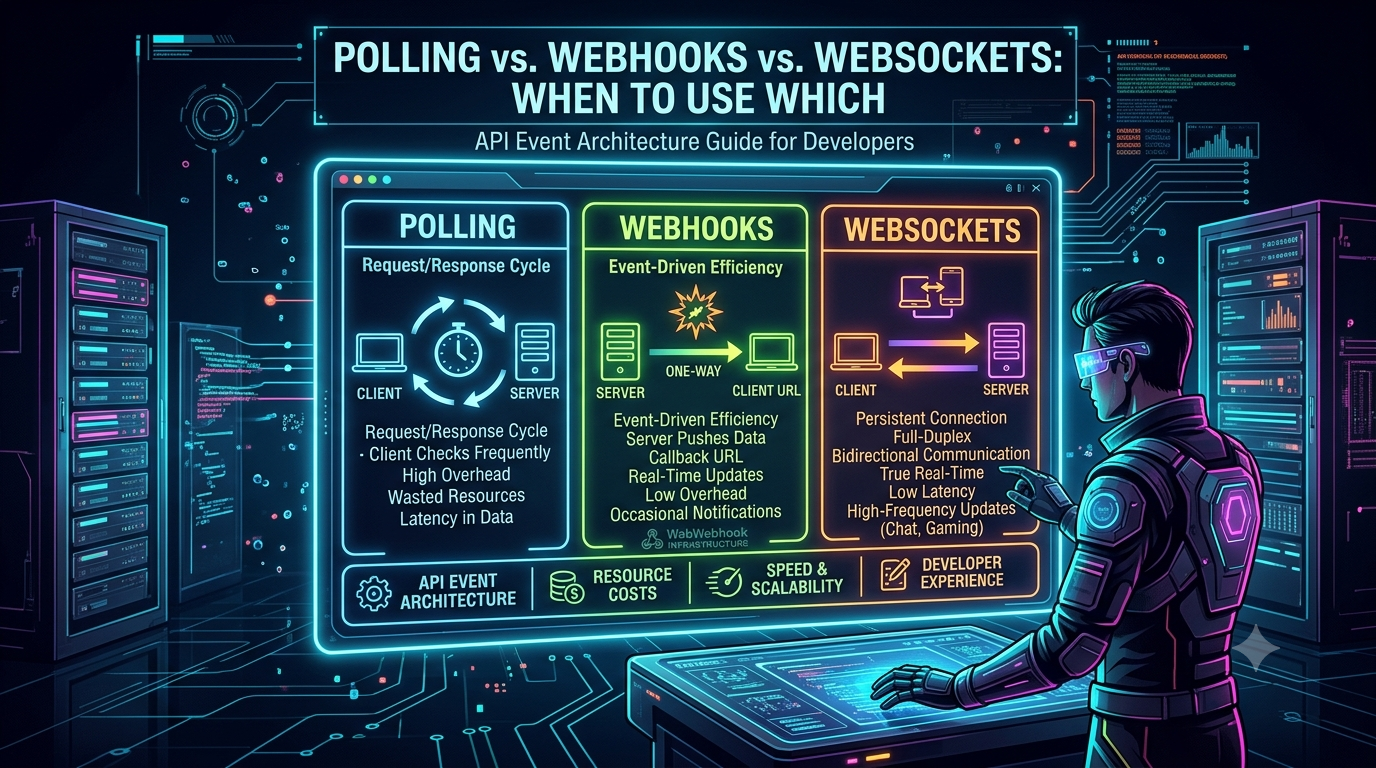
Polling vs. Webhooks vs. WebSockets vs. SSE: Choosing the Right Real-Time Architecture Choosing how your systems communicate state changes is one of the most consequential...

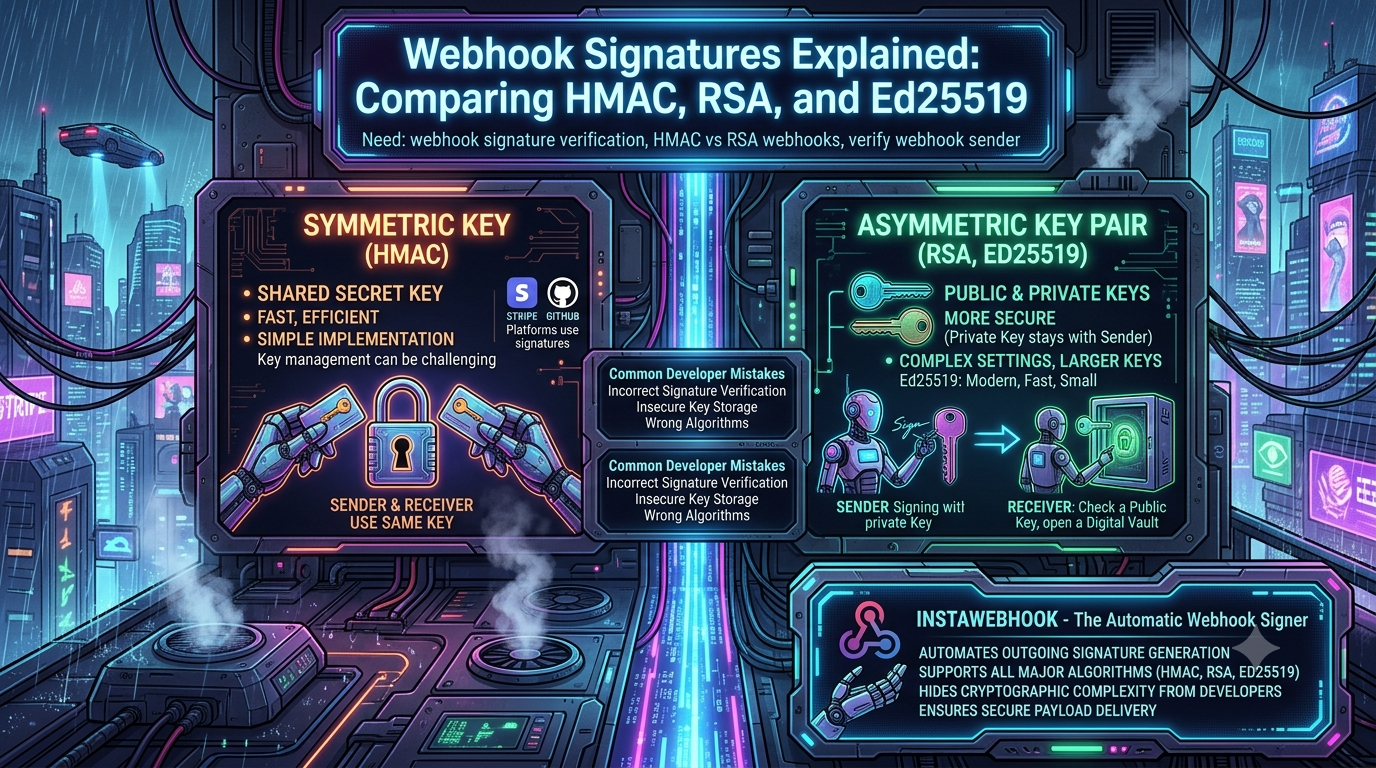
Webhook Signatures Explained: HMAC vs RSA vs Ed25519 The silent vulnerability in your API infrastructure Webhooks are the backbone of modern event-driven architectures.

Managing GitHub Actions Webhooks for Mission-Critical CI/CD: Building a Zero-Data-Loss Ingress Pipeline In modern platform engineering, GitHub webhooks act as the central nervous...

Scaling HubSpot Webhooks: Syncing CRM Data Without Dropping Leads When your company runs a high-converting marketing campaign, launches a product feature, or imports a major...

Building a HIPAA & SOC 2 Compliant Webhook Architecture: An Enterprise Guide In modern enterprise B2B SaaS, webhooks are no longer just an HTTP POST notification mechanism —...

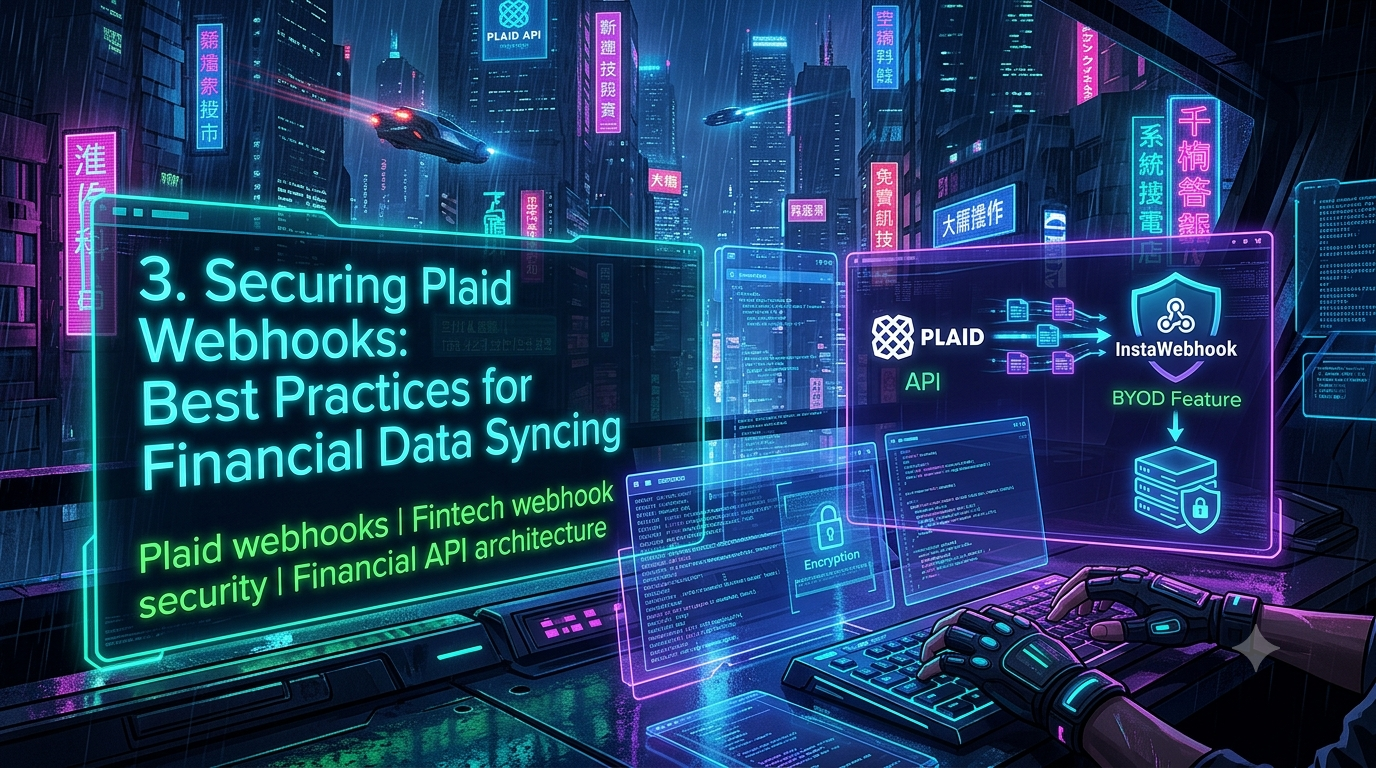
Securing Plaid Webhooks: Best Practices for Financial Data Syncing and Data Sovereignty In modern financial technology, real-time data sync is no longer optional — it's a core...

API Gateway vs. Webhook Ingress: Why Your Gateway Isn't Enough The modern software ecosystem runs on events.

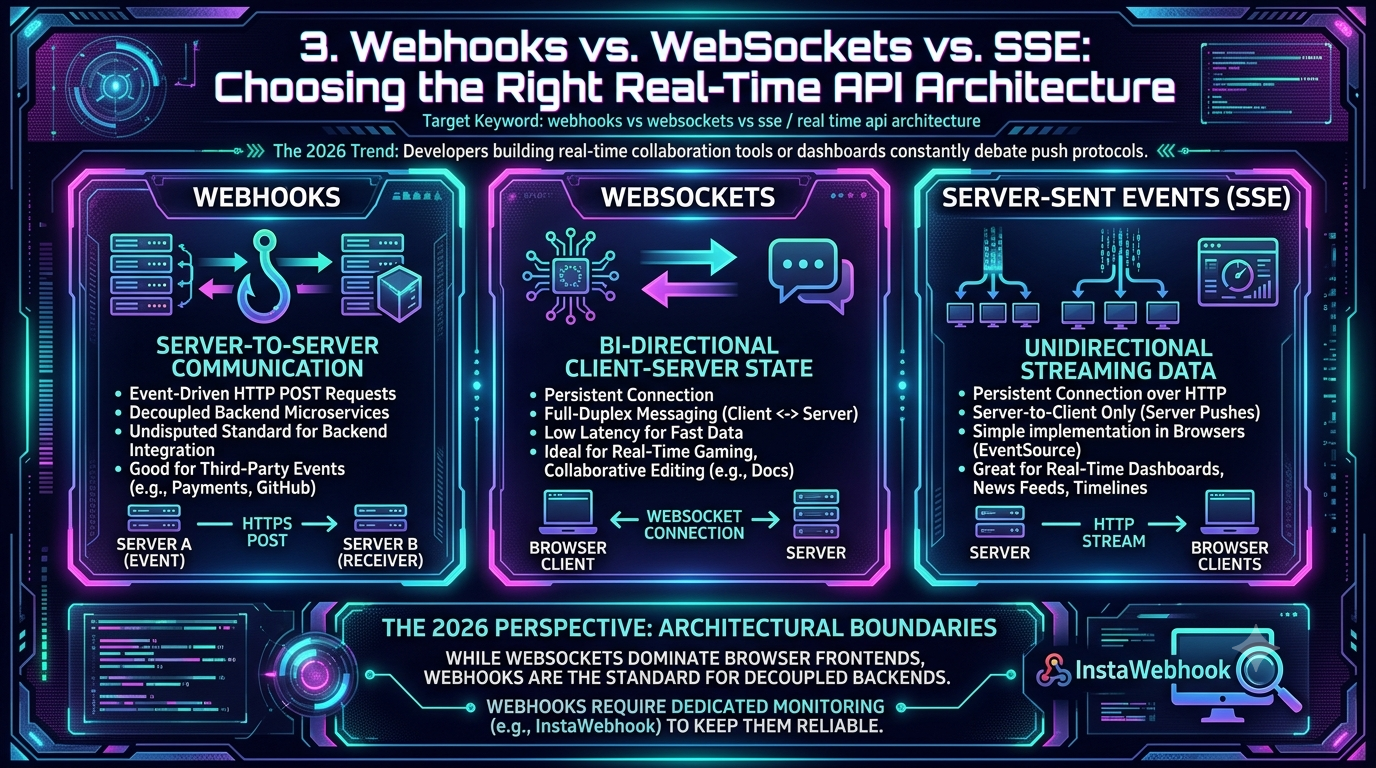
Webhooks vs. WebSockets vs. SSE: Choosing the Right Real-Time API Architecture Building real-time applications — interactive dashboards, collaborative whiteboards, live financial...

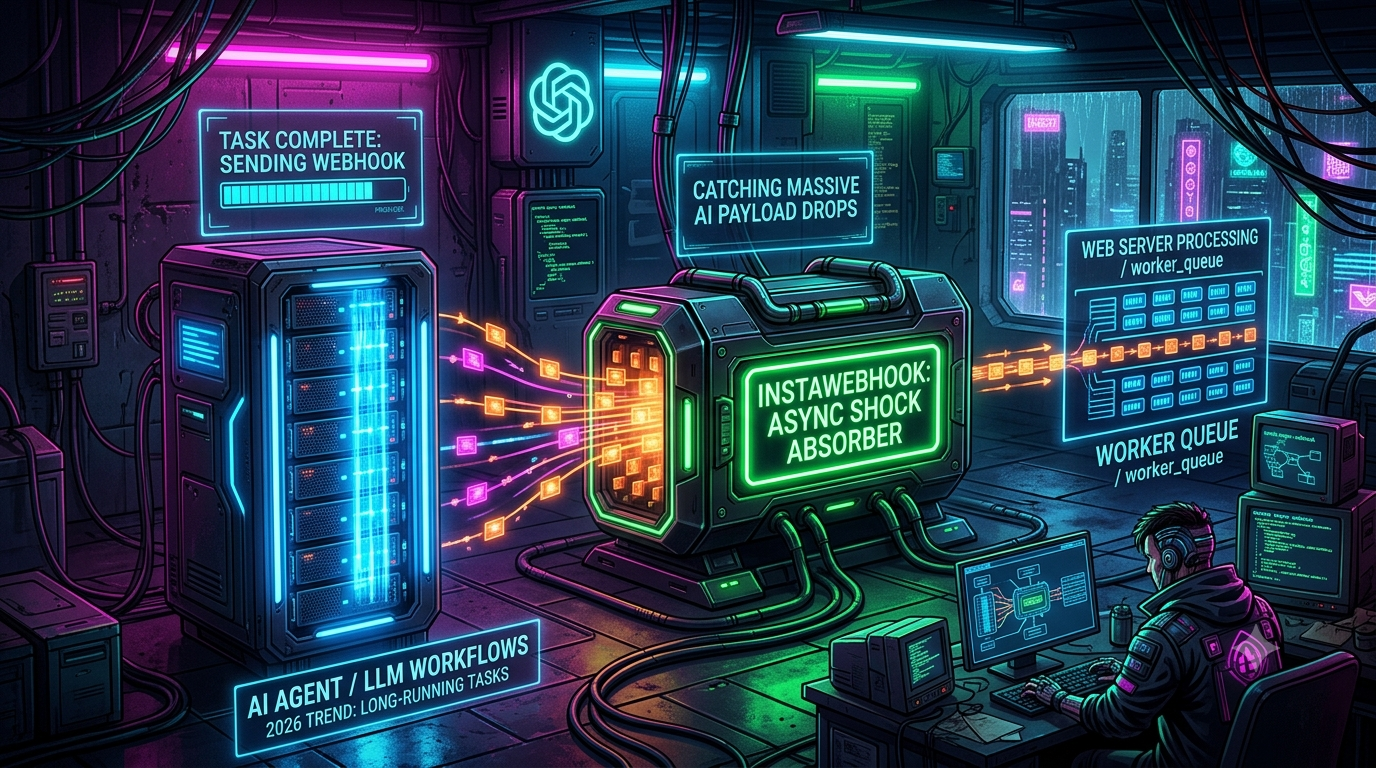
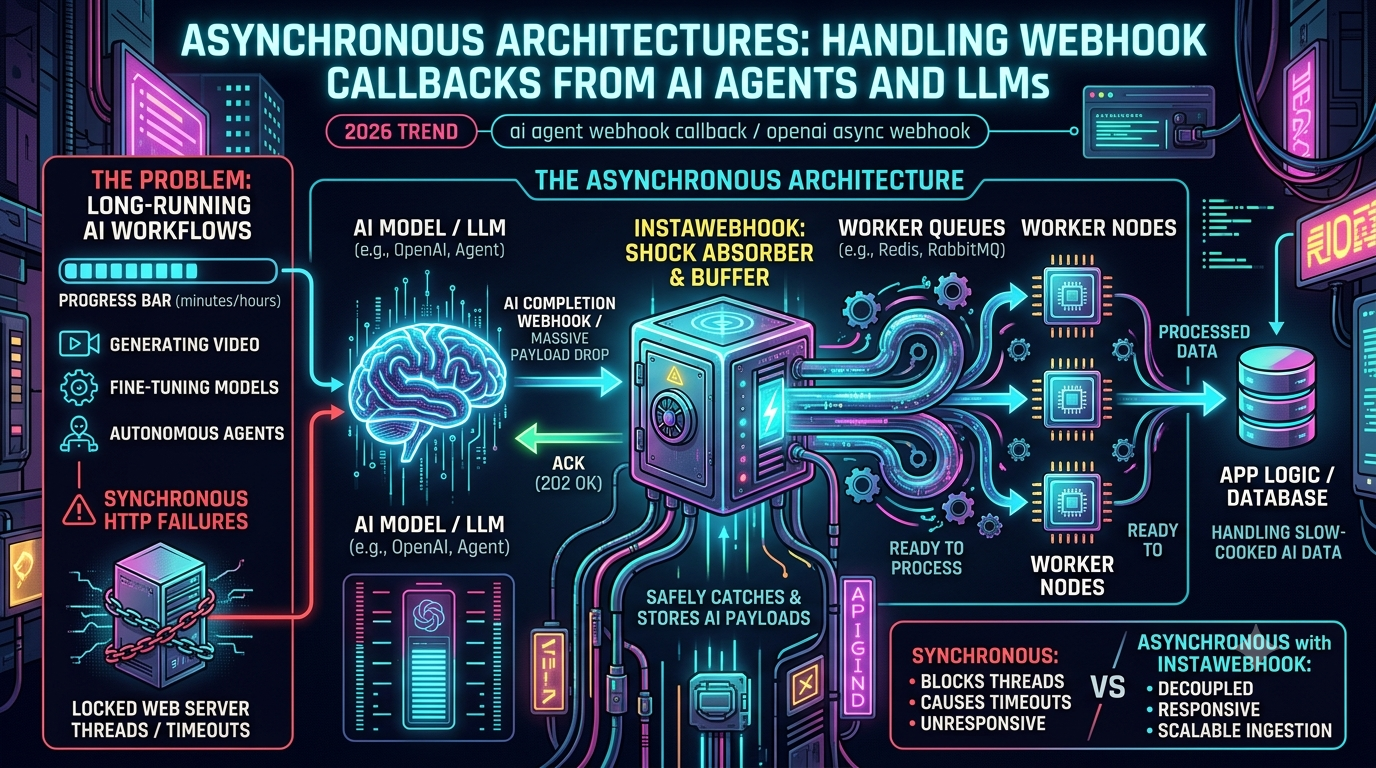
Asynchronous Architectures: Handling Webhook Callbacks from AI Agents and LLMs The early days of LLM apps were simple: send a prompt, wait a couple of seconds, get text back.

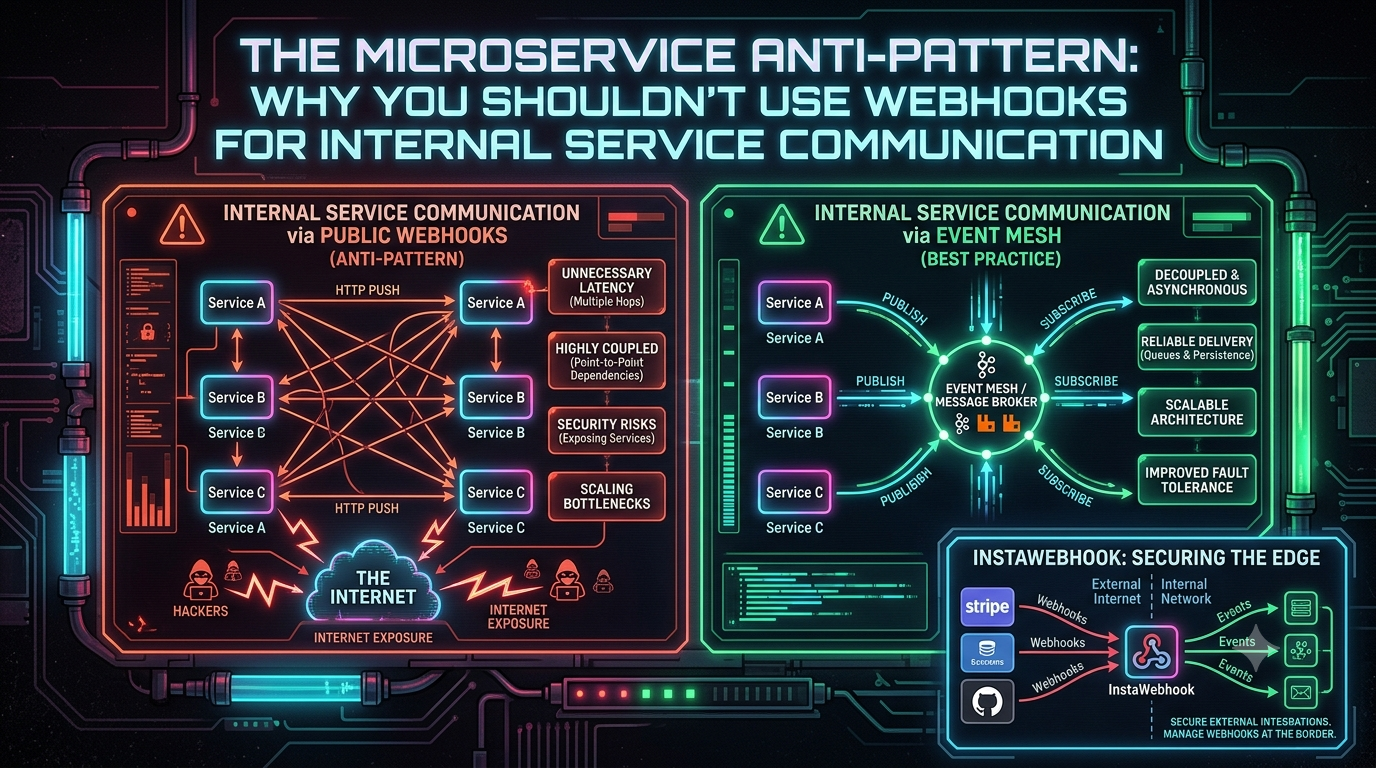
The Internal Webhooks Anti-Pattern: Why Service-to-Service HTTP Callbacks Don't Scale Microservices were supposed to make systems easier to change independently.

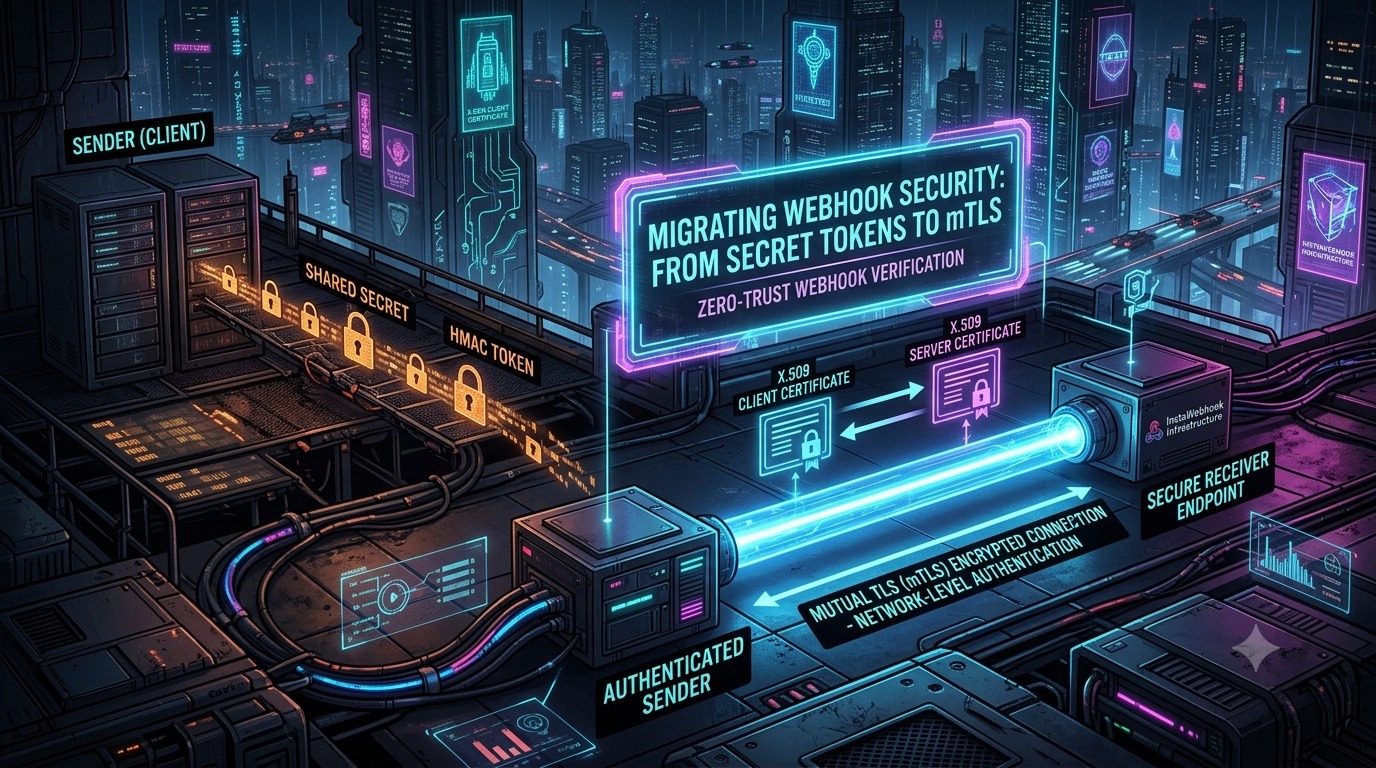
Zero-Trust Webhook Security: HMAC, mTLS, and What Actually Ships in 2026 Webhooks are one of the few pieces of internet plumbing that break the normal trust model of the web.

Webhooks vs. WebSockets vs. SSE: Choosing the Right Real-Time API Architecture Real-time features are no longer a "nice to have" — they're the baseline users expect from...

Asynchronous Architectures: Handling Webhook Callbacks from AI Agents and LLMs The landscape of AI integration has shifted.

Why Your Webhooks Keep Failing: A 2026 Debugging Guide Webhooks are the nervous system of the modern internet.

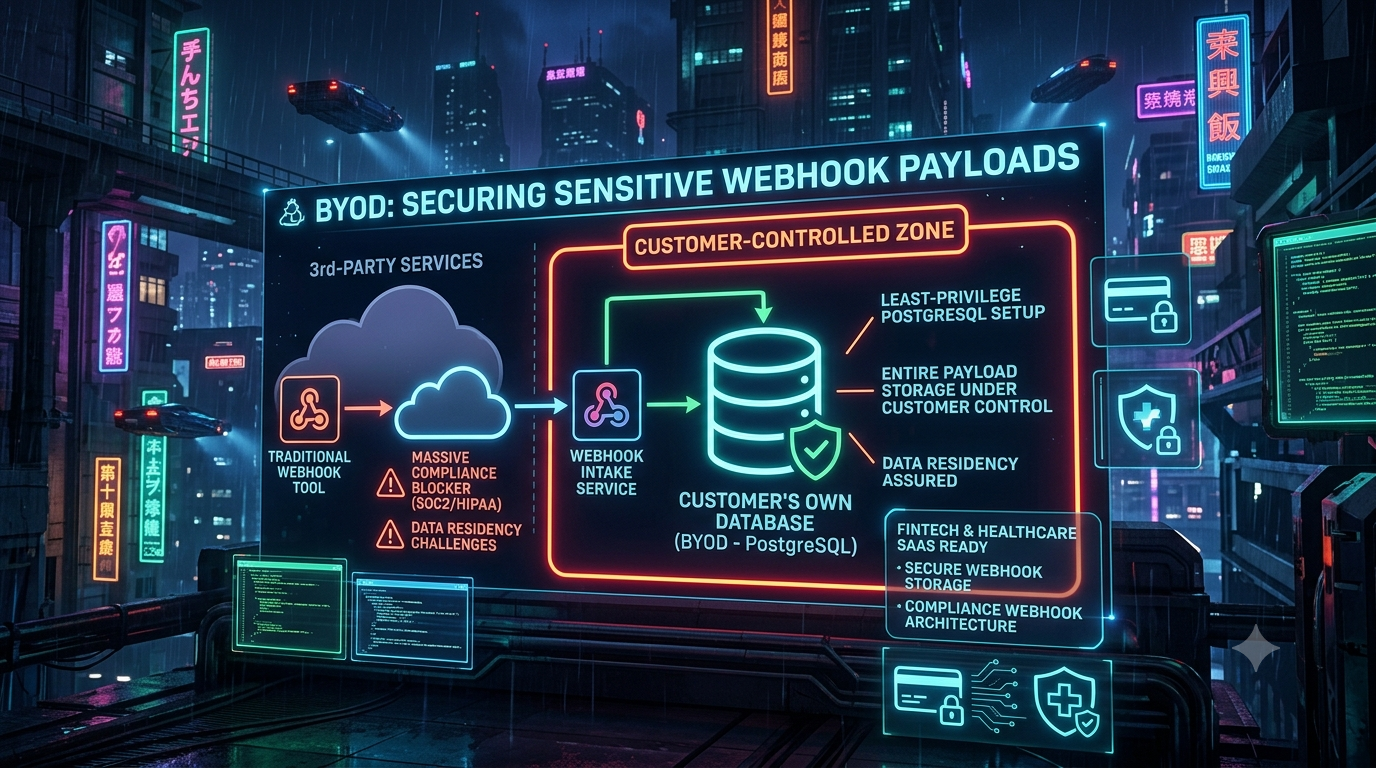
Bring Your Own Database (BYOD): Securing Sensitive Webhook Payloads Introduction Webhooks are the connective tissue of the modern internet.

Why Your Stripe Webhooks Keep Failing (And How to Fix Them for Good) If you've ever opened your Stripe Dashboard to find a red "failed" badge next to a webhook delivery, you...

Webhooks are the quiet infrastructure behind most modern integrations